Sentinel
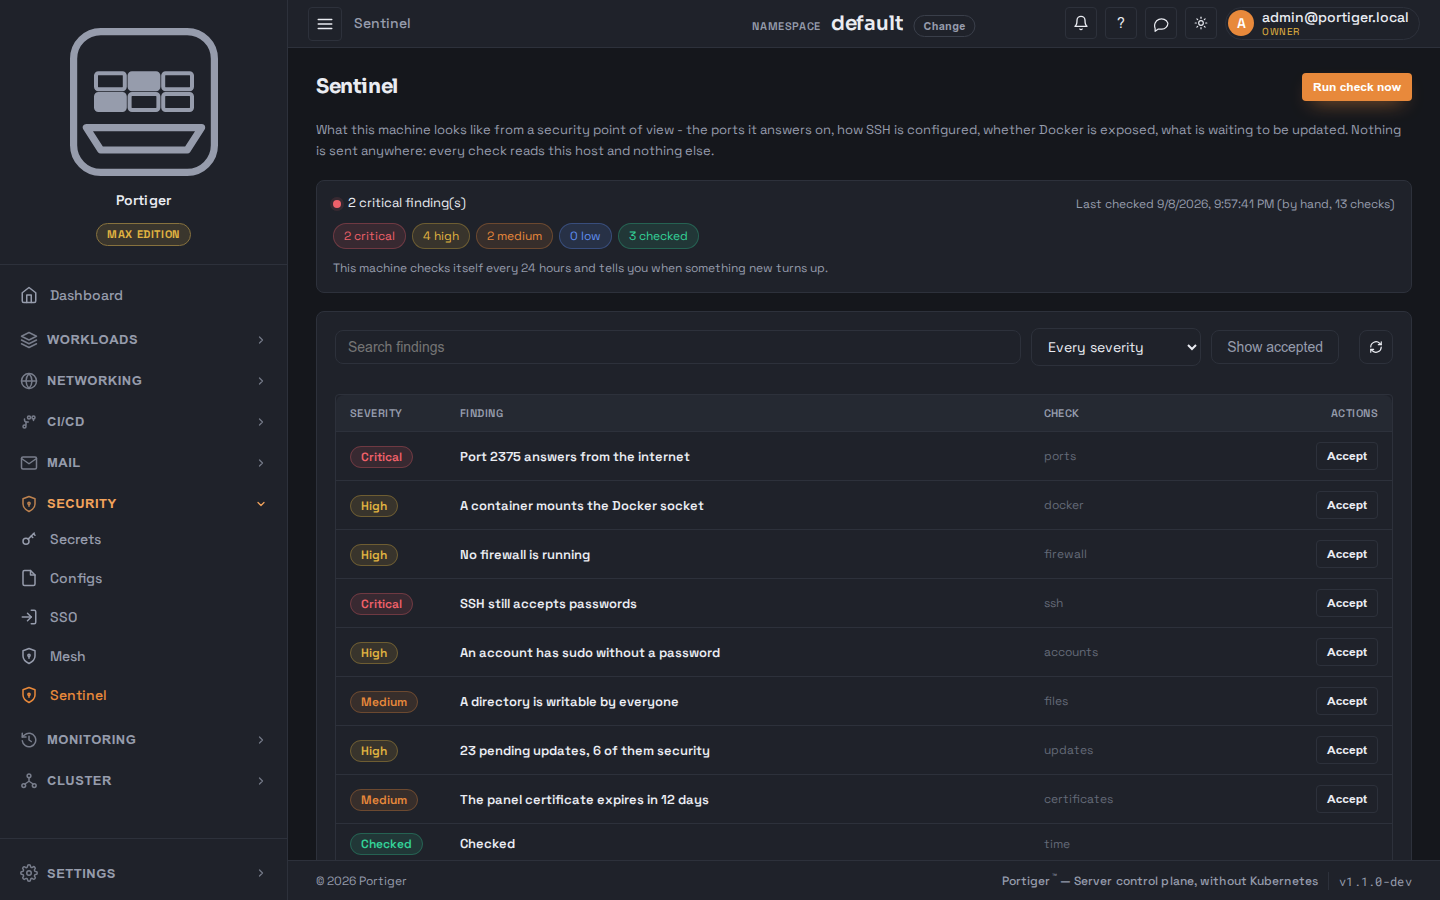
Sentinel reads this host's own configuration and tells you what is wrong with it: the ports it answers on, how SSH is set up, whether the Docker daemon is exposed, what is waiting to be updated. Nothing is sent anywhere. There is no scanner, no vulnerability database and no network traffic - it is this machine, read locally.
What it checks
Open ports, Docker daemon exposure, the firewall, SSH hardening, accounts and sudo, file permissions and SUID, kernel hardening, pending security updates, certificate expiry, failed login attempts, clock synchronisation, audit logging and the kernel version.
Severities
Critical, High, Medium, Low, and Checked for a check that found nothing wrong - which is shown, because a check that passed is information too.
Running it
Run check now reads this host and takes a few seconds. On Team and Max it also runs on its own every day and tells you when something new turns up; you can wire that into a notification channel. On Personal it runs when you ask for it. Every report is kept, with when it started, whether a person or the schedule started it, whether it was the full set or the basic one, and the counts per severity.
Accepting a finding
Some findings are things you have decided to live with. Accept asks for one line saying why, records it against the finding with your name, and takes it out of the counts. It comes back if the evidence changes - accepting the state of the machine is not the same as silencing the check.
What each plan runs
| Plan | Sentinel |
|---|---|
| Community | Not included |
| Personal | Four checks, on demand: open ports, SSH, the Docker daemon and pending updates |
| Team | Every check, daily, with notification |
| Max | Every check, daily, with notification |
On Personal the page names the checks that did not run rather than hiding that they exist. On Community it says Sentinel is not part of the plan.